Vulnerability handling
*[PSIRT]: Product Security Incident Team *[VDP]: Vulnerability Disclosure Policy
Reporting
Follow the Linaro Vulnerability Disclosure Policy (VDP), also published by security.txt (according to RFC 9116).
If you think you have found a security vulnerability in the LAA product or in its infrastructure, send an email to the Linaro Product Security Incident Team (PSIRT) at psirt@linaro.org. We will do our best to respond and fix any issues as soon as possible.
When reporting, please include:
the affected component of the LAA
the LAA version
steps to reproduce the issue
exploit code, if available
As with any bug, the more information you give, the easier it’s to diagnose and fix.
If you have plans for disclosing the vulnerability, tell us, since they may affect how we plan our own disclosure. Mark any sensitive information you do not want shared. We reserve the right to share what you send with trusted third parties and eventually the public, unless you ask us not to.
If we consider the report not to be a security vulnerability, we will inform you and direct the bug to the normal support process.
Scope
In scope: the LAA software stack and the LAA infrastructure.
Out of scope:
third-party dependencies; report those to their maintainers
operator-configured deployments; misconfiguration of the host system is the operator’s responsibility
Process
The Linaro PSIRT handles reports in five steps.
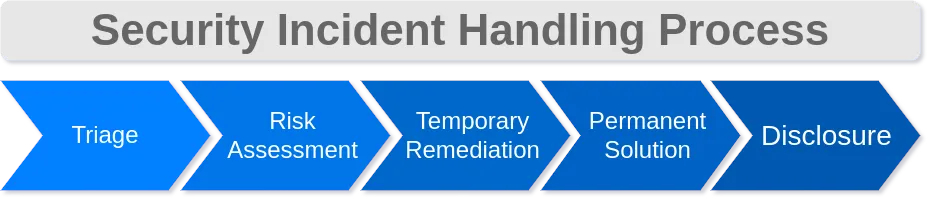
Triage. We assess the report to understand the potential impact.
If we can reproduce the vulnerability, we carry the process through to disclosure.
If we can’t reproduce it, we inform you and close the report.
If we consider the report not to be a security vulnerability, we inform you and direct the bug to the normal support process.
Risk assessment. We decide whether to fix the vulnerability in the product or address it another way, for example through risk acceptance or transference such as a configuration change.
Temporary remediation. We decide if and how the vulnerability can be mitigated in the meantime, before we work on a permanent solution.
Permanent solution. If we decided to fix the vulnerability in the product, we fix it as soon as possible. We will work with you to decide whether the fix goes out as a hotfix, in a monthly support release, or, depending on the impact and risk, in a major release.
Disclosure. We communicate the vulnerability as appropriate, for example by notifying affected users only or by publishing a public security advisory.
We also review each vulnerability afterwards and fold what we learn into our processes and products.
Disclosure
Please don’t disclose the vulnerability publicly until a fix has been released.
Frequently asked questions
Do you have a bug bounty program? The LAA project or Linaro doesn’t offer a bug bounty program.